Hall of Fame
Vendors that have acknowledged and patched responsibly disclosed vulnerabilities.
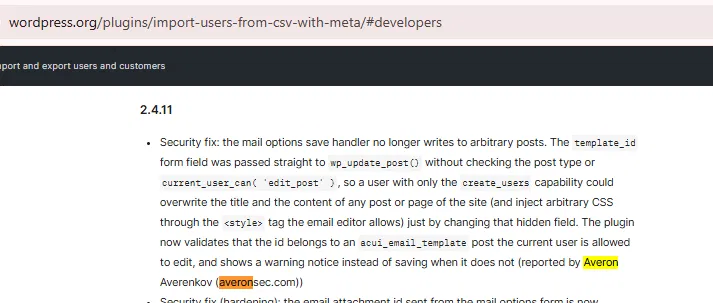
WordPress Plugin Vendor - Import/Export Users & Customers
"This bug is also fixed now... The new version fixes three issues in one go. Thanks again for your help." - credited in changelog as "reported by Averon Averenkov (averonsec.com)"
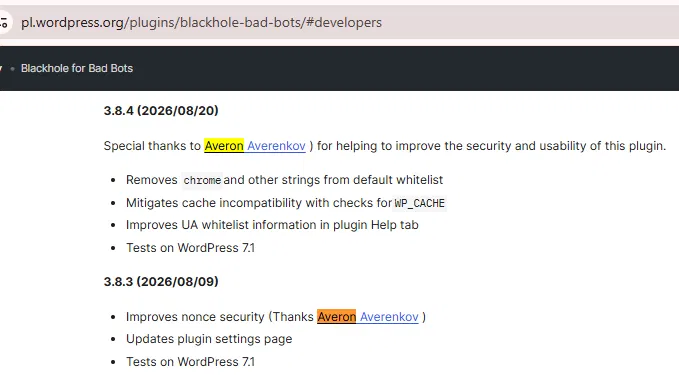
WordPress Plugin Vendor - Blackhole for Bad Bots
"Special thanks to Averon Averenkov" - credited in changelog across two consecutive releases
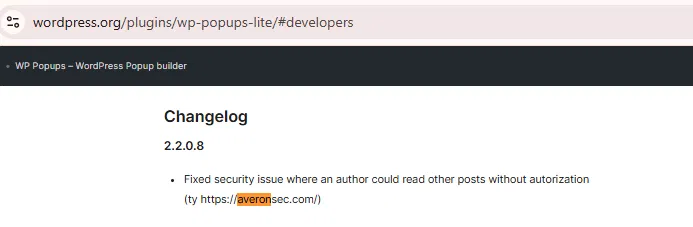
WordPress Plugin Vendor - WP Popups
"ty https://averonsec.com/" - credited directly in the changelog
WordPress Plugin Vendor - Log Import Handler
"Thank you very much for your help. This issue is already solved, and it will be released with version 2.2.2."
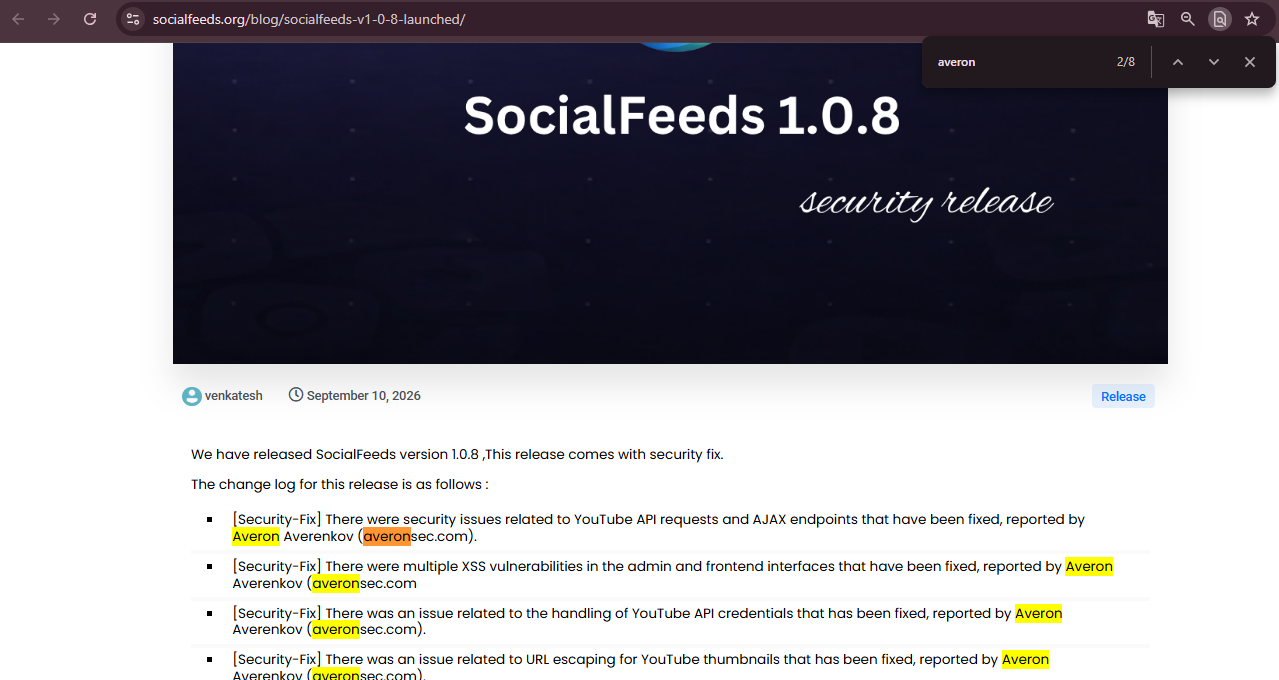
WordPress Plugin Vendor - Social Media Feed Display
"There were security issues related to YouTube API requests and AJAX endpoints that have been fixed, reported by Averon Averenkov (averonsec.com)." - dedicated security release blog post, 4 issues credited
WordPress Plugin Vendor - User Role Editor
"Sorry for the late reply. I'll include it. Thanks."
Patchstack Vulnerability Disclosure Program
Six confirmed reports patched through coordinated disclosure, spanning SQL Injection,
Broken Access Control, and Information Exposure across the WordPress plugin ecosystem.
Wordfence Vulnerability Disclosure Program
Two additional reports validated and publicly disclosed through Wordfence's threat intelligence pipeline -
a Stored XSS and a Missing Authorization / sensitive information disclosure issue.
Vendor names are withheld by default in line with my responsible disclosure policy -
full technical detail available on request or via the
Patchstack or
Wordfence public records.
← Back to main page